Tag: Cyber Espionage

FBI Warns FSB-Linked Hackers Exploiting Unpatched Cisco Devices for Cyber Espionage
News

FBI Warns FSB-Linked Hackers Exploiting Unpatched Cisco Devices for Cyber Espionage

A seven-year-old security hole in Cisco IOS and Cisco IOS XE software has been regularly exploited by Static Tundra, a Russian state-sponsored cyber espionage group, to gain continuous access to target networks. According to Cisco Talos, which made the activity public, the attacks target companies in the manufacturing, telecommunications, and higher education sectors in North America, Asia, Africa, and Europe. According to the statement, recent efforts have been made against Ukraine and its allies since the start of the Russo-Ukrainian war in 2022, and prospective victims are selected based on their "strategic interest" to Russia. The vulnerability in question is CVE-2018-0171 (CVSS score: 9.8), a serious weakness in Cisco IOS Software and Cisco IOS XE software's Smart Install capab...
Joint Advisory Warns of PRC-Backed Cyber Espionage Targeting Telecom Networks
News

Joint Advisory Warns of PRC-Backed Cyber Espionage Targeting Telecom Networks

Threat actors with ties to the People's Republic of China (PRC) have launched a widespread cyber espionage campaign against telecommunications companies, according to a joint alert released by the U.S., Canada, New Zealand, and Australia. According to government authorities, no new activity has been noticed; the identified exploitations or compromises linked to the activity of these threat actors are consistent with pre-existing vulnerabilities related to victim infrastructure. About six months after a probe into the intrusions began, U.S. officials said Tuesday that the threat actors are still active within U.S. telecommunications networks read more about Joint Advisory Warns of PRC-Backed Cyber Espionage Targeting Telecom Networks. Get up to date on the latest cybersecurity new...
Chinese State-Backed Cyber Espionage Targets Southeast Asian Government
News

Chinese State-Backed Cyber Espionage Targets Southeast Asian Government

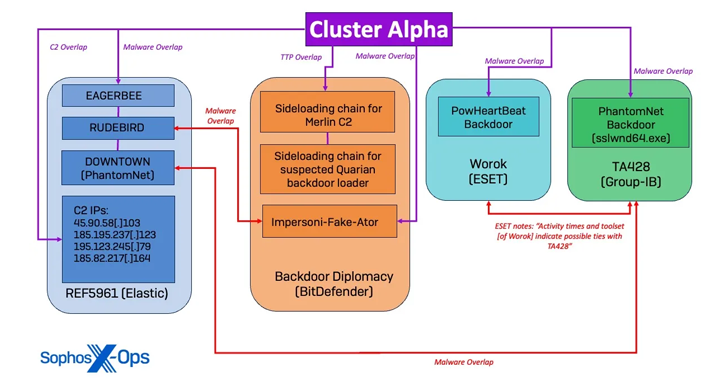
An unidentified prominent government agency in Southeast Asia became the focus of a "complex, long-running" state-supported cyberespionage campaign backed by China, known by the codename Crimson Palace. In a report shared with The Hacker News, Sophos researchers Paul Jaramillo, Morgan Demboski, Sean Gallagher, and Mark Parsons stated that the campaign's overarching objective was to maintain access to the target network for cyberespionage in support of Chinese state interests. This entails getting into vital IT networks, spying on particular users, gathering private military and technical data, and installing different malware implants to facilitate command-and-control (C2) interactions. The government organization's name was not made public read more Chinese State-Backed Cyber Es...
Two Chinese APT Groups Ramp Up Cyber Espionage Against ASEAN Countries
News

Two Chinese APT Groups Ramp Up Cyber Espionage Against ASEAN Countries

Throughout the course of the last three months, two China-affiliated advanced persistent threat (APT) groups have been seen conducting cyberespionage against ASEAN members and relevant organizations. This includes the threat actor known as Mustang Panda, who was recently connected to cyberattacks using the DOPLUGS backdoor variant of PlugX (also known as Korplug) against Myanmar and other Asian nations. Mustang Panda, also known as Camaro Dragon, Earth Preta, and Stately Taurus, is thought to have sent phishing emails containing two malware packages to organizations in Singapore, Japan, the Philippines, and Myanmar. Malware for these packages was produced by threat actors on March 4-5, 2024, which also happened to be the dates of the ASEAN-Australia Special Summit read more Two C...
U.S. Government Blacklists Cytrox and Intellexa Spyware Vendors for Cyber Espionage
News

U.S. Government Blacklists Cytrox and Intellexa Spyware Vendors for Cyber Espionage

Tuesday, the U.S. government put Cytrox and Intellexa, two foreign commercial spyware providers, on an economic blacklist for "threatening [ing] the privacy and security of individuals and organizations worldwide" by weaponizing cyber vulnerabilities to gain unauthorized access to equipment. This covers the businesses' corporate assets in North Macedonia (Cytrox AD), Greece (Intellexa S.A.), Ireland (Intellexa Limited), and Hungary (Cytrox assets Crt). It forbids U.S. companies from doing business with these organizations by placing them to the economic denylist. The Commerce Department's action today targets these entities' ability to access commodities, software, and technology that could contribute to the development of surveillance tools that pose a risk of misuse in violations ...