Tag: Remcos RAT

New Malware Campaign Delivers Remcos RAT Through Multi-Stage Windows Attack
News

New Malware Campaign Delivers Remcos RAT Through Multi-Stage Windows Attack

Cybersecurity experts have revealed information on a new campaign called SHADOW#REACTOR, which uses an evasive multi-stage attack chain to create persistent, covert remote access and deliver Remcos RAT, a commercial remote administration tool. According to a technical report shared with The Hacker News by Securonix researchers Akshay Gaikwad, Shikha Sangwan, and Aaron Beardslee, the infection chain follows a carefully planned execution path: an obfuscated VBS launcher run via wscript.exe triggers a PowerShell downloader, which retrieves fragmented, text-based payloads from a remote host. A.NET Reactor-protected assembly reconstructs these pieces into encoded loaders, decodes them in memory, and uses them to retrieve and apply a distant Remcos configuration. The Remcos RAT backdoor i...
New IDAT Loader Attacks Using Steganography to Deploy Remcos RAT
News

New IDAT Loader Attacks Using Steganography to Deploy Remcos RAT

As part of a malicious effort, Finnish-based Ukrainian organizations have been targeted for the distribution of Remcos RAT, a commercial remote access trojan, via the use of the malware loader IDAT Loader. A threat actor known as UAC-0184 which is being monitored by the Computer Emergency Response Team of Ukraine (CERT-UA) is believed to be responsible for the attack. According to a report provided with The Hacker News by Morphisec researcher Michael Dereviashkin, "the attack, as part of the IDAT Loader, used steganography as a technique. Even though steganographic, or "Stego," techniques are widely recognized, it's crucial to comprehend how they contribute to defense evasion to better grasp how to counter such strategies read more New IDAT Loader Attacks Using Steganography to Depl...
Remcos RAT Spreading Through Adult Games in New Attack Wave
News

Remcos RAT Spreading Through Adult Games in New Attack Wave

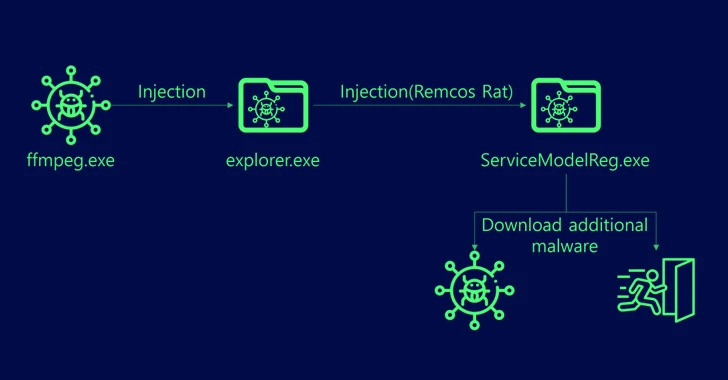
In South Korea, webhards have been used to spread the Remcos remote access trojan (RAT), which is masquerading as adult-themed games. Throughout the nation, people upload, download, and exchange files via WebHard, also known as web hard drive. Although webhards have been used to propagate DDoS botnet malware, UDP RAT, and njRAT in the past, the most recent investigation from the AhnLab Security Emergency Response Center (ASEC) reveals that Remcos RAT has been distributed using this technique. These assaults pose as adult games to fool users into accepting booby-trapped files that, when opened, allow malicious Visual Basic scripts read more Remcos RAT Spreading Through Adult Games in New Attack Wave. Get up to date on the latest cybersecurity news and enhance your knowledge of ...
UAC-0050 Group Using New Phishing Tactics to Distribute Remcos RAT
News

UAC-0050 Group Using New Phishing Tactics to Distribute Remcos RAT

The threat actor known as UAC-0050 uses novel techniques to avoid detection by security products in order to propagate Remcos RAT through phishing attempts. According to Uptycs security experts Karthickkumar Kathiresan and Shilpesh Trivedi, "the group's weapon of choice is Remcos RAT, a notorious malware for remote surveillance and control, which has been at the forefront of its espionage arsenal." The report was released on Wednesday. "However, in their latest operational twist, the UAC-0050 group has integrated a pipe method for interprocess communication, showcasing their advanced adaptability." Active since 2020, UAC-0050 has a history of using social engineering tactics to fool victims into opening infected attachments read more UAC-0050 Group Using New Phishing Tactics to D...
Fruity Trojan Uses Deceptive Software Installers to Spread Remcos RAT
News

Fruity Trojan Uses Deceptive Software Installers to Spread Remcos RAT

To fool unwary users into downloading Fruity, a malware downloader, in order to install remote trojan tools like Remcos RAT, threat actors create bogus websites providing trojanized software installations. The software in question includes, according to a study by cybersecurity provider Doctor Web, "a variety of tools for fine-tuning CPUs, graphic cards, and BIOS; PC hardware-monitoring tools; and some other apps." Such installers serve as a ruse since they include the trojan together with all of its components in addition to the program that potential victims would be interested in read more Fruity Trojan Uses Deceptive Software Installers to Spread Remcos RAT. Stay informed with the best cybersecurity news and raise your cybersecurity awareness with our comprehensive coverage o...