Tag: South Korea

US and South Korea warn of Gunra ransomware targeting govt agencies
News

US and South Korea warn of Gunra ransomware targeting govt agencies

The National Policy Agency of South Korea and federal agencies in the United States issued a warning to governments and critical infrastructure companies around the world to protect their systems from Gunra ransomware assaults. The ransomware organization targets a variety of business sectors, including public health, healthcare, finance, and government services, using a malware variant based on the Conti ransomware source code that was disclosed in February 2022, according to a joint advisory released on Monday. According to the authoring authorities, Gunra initially surfaced in April 2025 as a sophisticated double-extortion ransomware version that was taken from the stolen Conti1 ransomware source code. The FBI saw Gunra actors attempting, with varying degrees of success, to send ...
South Korea Suspends DeepSeek AI Downloads Over Privacy Violations
News

South Korea Suspends DeepSeek AI Downloads Over Privacy Violations

The Chinese artificial intelligence (AI) chatbot DeepSeek has been officially prohibited from being downloaded in South Korea unless the company updates its mobile apps to adhere to data protection laws. As of February 15, 2025, at 6:00 p.m. local time, downloads have been suspended, according to a statement from the Personal Information Protection Commission (PIPC). The web service is still available. According to the agency, it started analyzing DeepSeek on its own immediately after it launched and found some flaws in its communication features and third-party service providers' regulations for the use of personal data read more about South Korea Suspends DeepSeek AI Downloads Over Privacy Violations. Get up to date on the latest cybersecurity news and enhance your knowledge of...
South Korea Fines Meta $15.67M for Illegally Sharing Sensitive User Data with Advertisers
News

South Korea Fines Meta $15.67M for Illegally Sharing Sensitive User Data with Advertisers

The data privacy authority in South Korea has fined Meta 21.62 billion won ($15.67 million) for unlawfully gathering private information from Facebook users, such as their sexual orientation and political beliefs, and disclosing it to marketers without their permission. According to the nation's Personal Information Protection Commission (PIPC), Meta collected data from approximately 980,000 domestic Facebook users, including their political beliefs, religious affiliations, and same-sex marriage status, and distributed it to 4,000 advertisers. According to a news release from the PIPC, it was discovered that behavioral data—such as the Facebook sites users "liked" and the advertisements they clicked on—was examined to develop and run advertising campaigns pertaining to sensitive dat...
North Korean Hackers Deploy New Golang Malware ‘Durian’ Against Crypto Firms
News

North Korean Hackers Deploy New Golang Malware ‘Durian’ Against Crypto Firms

A previously unreported Golang-based malware known as Durian has been seen being used by the North Korean threat actor known as Kimsuky in highly focused cyberattacks against two South Korean bitcoin companies. According to Kaspersky's APT trends report for Q1 2024, "Durian boasts comprehensive backdoor functionality, enabling the execution of delivered commands, additional file downloads, and file exfiltration." The genuine software that was only available in South Korea was utilized as an infection channel in the August and November 2023 attacks. The specific method by which the product was manipulated is still unknown. It is known that the software connects to the attacker's site and retrieves a malicious payload, which initiates the infection process read more North Korean Ha...
Kimsuky’s New Golang Stealer ‘Troll’ and ‘GoBear’ Backdoor Target South Korea
News

Kimsuky’s New Golang Stealer ‘Troll’ and ‘GoBear’ Backdoor Target South Korea

Kimsuky, a nation-state actor with ties to North Korea, is suspected of deploying Troll Stealer, an information stealer built on Golang that was previously unreported. In a recent technical analysis, South Korean cybersecurity company S2W stated that the malware pilfers "SSH, FileZilla, C drive files/directories, browsers, system information, [and] screen captures" from compromised devices. Troll Stealer's connections to Kimsuky are based on the malware's resemblances to well-known families, like AppleSeed and AlphaSeed, which have been linked to the gang. Kimsuky, also known as APT43, ARCHIPELAGO, Black Banshee, Emerald Sleet (formerly known as Thallium), Nickel Kimball, and Velvet Chollima, is a notorious hacker that is frequently used in offensive cyber operations to acquire p...
Remcos RAT Spreading Through Adult Games in New Attack Wave
News

Remcos RAT Spreading Through Adult Games in New Attack Wave

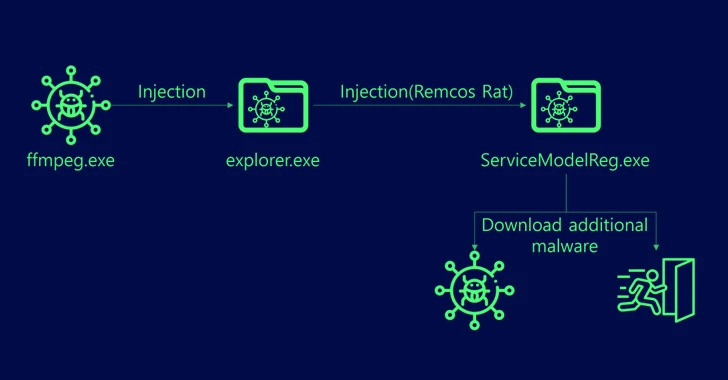
In South Korea, webhards have been used to spread the Remcos remote access trojan (RAT), which is masquerading as adult-themed games. Throughout the nation, people upload, download, and exchange files via WebHard, also known as web hard drive. Although webhards have been used to propagate DDoS botnet malware, UDP RAT, and njRAT in the past, the most recent investigation from the AhnLab Security Emergency Response Center (ASEC) reveals that Remcos RAT has been distributed using this technique. These assaults pose as adult games to fool users into accepting booby-trapped files that, when opened, allow malicious Visual Basic scripts read more Remcos RAT Spreading Through Adult Games in New Attack Wave. Get up to date on the latest cybersecurity news and enhance your knowledge of ...
South Korean crypto exchange GDAC hacked for nearly $14M
News

South Korean crypto exchange GDAC hacked for nearly $14M

The GDAC cryptocurrency exchange in South Korea was breached, losing over $13.9 million in cryptocurrency. In reaction to the attack, the exchange has paused all deposits and withdrawals and is carrying out urgent server repair, according to a statement made by GDAC CEO Han Seunghwan on April 10. The notification states that the attacker took control of a few of the exchange's hot wallets on April 9 in the early morning and started moving cryptocurrency into those wallets at 7 am Korean Standard Time. The hack resulted in the theft of about 61 Bitcoin, 350.5 Ether, 10 million units of the WEMIX virtual currency, and $220,000 worth of Tether. At the pricing of April 10, this equates to almost $13.9 million in cryptocurrency read more South Korean crypto exchange GDAC hacked for nearly $...
FakeCalls Android Malware Targets Financial Firms in South Korea
News

FakeCalls Android Malware Targets Financial Firms in South Korea

A new Android voice phishing (vishing) malware tool has been discovered that targets victims in South Korea by pretending to be 20 of the country's top financial institutions. The software, dubbed "FakeCalls" by the Check Point Research (CPR) team, lures victims with false loans and asks them to confirm their credit card information so that their information can be taken. "FakeCalls malware boasts the functionality of a Swiss army knife, able not only to conduct its primary purpose but also to take private data read more Fake Calls Android Malware Targets Financial Firms in South Korea. Stay informed with the best cybersecurity news and raise your cybersecurity awareness with our comprehensive coverage of the latest threats, breaches, and solutions.